While refrigerators were getting hacked in Estonia, I half-seriously took a project I’m working on and asked Claude Code if there are any low-hanging fruit regarding security that we could improve. It found one issue that was easy to fix, simple oversight with a one line fix, so I just went along with it.
Then it got stopped because of bullshit “AI safeguards”. Oh no, how dare I, the senior product engineer with my product that I provably have control over, try to fix and prevent security issues and ensure compliance with local laws and regulations?
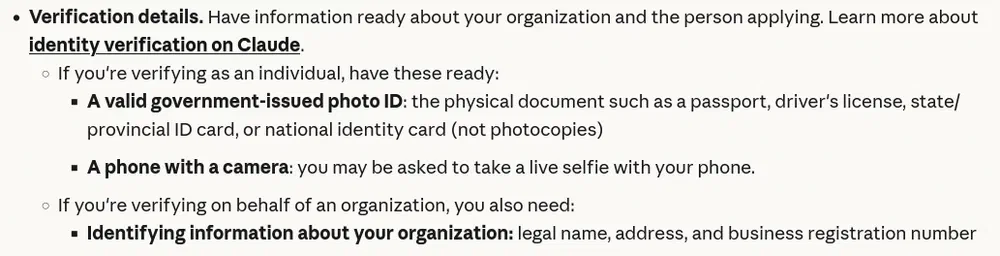
“Oh but you can just apply to get an exemption from them here bla bla fucking blah”
Have you READ the requirements?
First of all, you will have to wait for multiple business days to get a response.
You forfeit any data retention exemptions, so hope you don’t have any IP to protect!
Oh, and oh so please give us your fucking ID or passport! We won’t leak it later, promise!

And you may just get fucked anyway and not get approval. Approval to appropriately protect your own service!
This wasn’t the first time I ran into this issue. As maddening as it sounds, I try to keep up with the security landscape and to apply appropriate mitigations because leaking sensitive information is a big fucking no-no and I can’t let that happen.
If there’s a popular exploit out there that applies for our technical stack, I need to know if the public proof-of-concept snippets can be adapted and used maliciously against my services. But no, Claude will tell you to fuck off and use an older model that still will try to stop you from applying adequate protection.
You know who don’t need to ask for approval? Criminals. They just go and use the models that don’t have safeguards in place. Abliterated open weights models don’t care. Bad actors reach their goals with or without your “safe” models.
You can use a knife to cut up some food, or seriously hurt someone. Yet I don’t get asked to put in an application with my government-provided ID to buy one. Why is this tool so special?
Predictably, the only way to actually make our own service more secure ended up involving the use of EU-hosted open weights models, such as GLM 5.3, that actually complied with our intentions, proved that the issue is there, and then helped fix and verify that the issue is now resolved, for good.
Congratulations, Anthropic, you’ve made the world an unsafer place.
Or maybe that was your plan all along to get regulators to react and build that moat for you right before your IPO to fend off competitors?
Either way, I’m just incredibly frustrated. Big AI labs use the same tools without restrictions to make the security landscape a fucking mess, and then they go and prohibit others from using the same tools to protect themselves from the threats they just created. Fucking asshats.